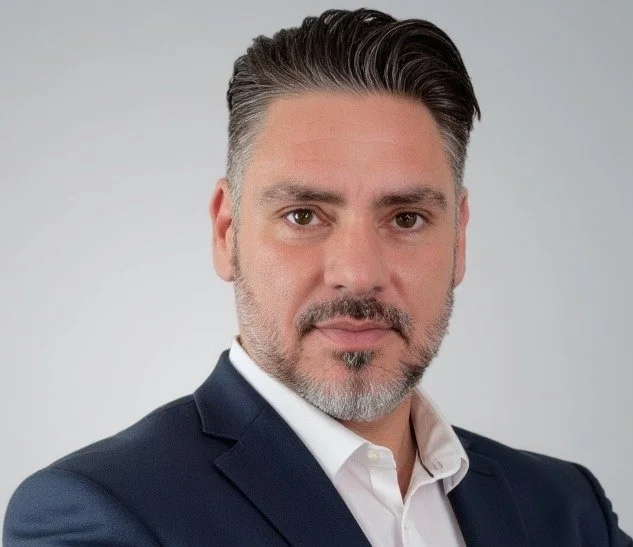
Clive Boonzaaier
Co-founder & COO
Clive has over twenty years of experience in cybersecurity and regulatory compliance.
Experience and background
Clive is a PCI DSS Qualified Security Assessor (QSA) and PCI Professional (PCIP – Payment Card Industry Professional), with extensive experience supporting PCI DSS compliance programmes, including 3-D Secure (3DS) environments. He is also an ISO/IEC 27001 Lead Auditor, Certified Information Security Manager (CISM), and CISMP certified. In addition, Clive has significant experience working with regulatory frameworks such as HIPAA, the Gramm–Leach–Bliley Act (GLBA), and the General Data Protection Regulation (GDPR) across regulated industries.
20 years
Martyn Martynowicz
Co-founder & CEO
Martyn has more than two decades of experience in the IT and information security sector.
Experience and background
Martyn is an ISO/IEC 27001 Lead Auditor and Lead Implementer and holds the qualification of PCI Professional (PCIP – Payment Card Industry Professional). He has extensive experience working with PCI DSS and NIST-aligned security frameworks and a strong background in developing and overseeing security programmes that protect the confidentiality, integrity, and availability of business-critical information.
20 years
Mark Daeche
Co-founder & Chair of the Board
Mark is a software engineer by training with decades of experience in the software industry.
Experience and background
Mark held senior management and executive roles within the global PC software industry across the United States and Europe. His career spans large-scale corporate environments as well as entrepreneurial ventures in technology-driven markets.
Celeste Roux
Director of Operations
Celeste has a professional background in operations, marketing, and sales, with formal experience in customer service management and commercial operations across multiple industries.
Experience and background
Celeste’s expertise spans operational oversight, customer engagement, and marketing support, enabling effective alignment between service delivery, sales functions, and organisational objectives.
Fiona Howard
Senior Cybersecurity Consultant
Fiona holds a Master’s degree in Information Security and is a PCI DSS Qualified Security Assessor (QSA), as well as an ISO/IEC 27001 Lead Auditor and Lead Implementer.
Experience and background
Fiona’s professional experience spans a range of IT and security environments, with a particular focus on PCI DSS certification and information security assurance.